Know when a product you run is on CISA’s exploited list
PatchAlert alerts you when a product you picked appears in the CISA Known Exploited Vulnerabilities catalog, and helps you track patching across your locations.
Early access: all features are free. Built for IT workers.
The Status ring in the app, cycling through its three states:
!3 open alerts, 1 overdue
▤4 to review
✓No open alerts
The catalog PatchAlert watches
exploited vulnerabilities in the catalog
1,781
products
741
vendors
295
added in the past 12 months
322
known to be used in ransomware campaigns
361
CISA Known Exploited Vulnerabilities catalog, version 2026.11.13, released November 13, 2026. PatchAlert checks the catalog every 6 hours; these numbers are from the version above.
How it works
Pick what you run. Choose products for each location, or follow a whole vendor.
Get an alert. When CISA adds an exploited vulnerability for one of them, PatchAlert sends a push notification (“Active exploitation:” and the product) with the CISA federal due date and the affected locations.
Record what you did. For each location, record patched, mitigated, not affected, or deferred with a review date. See what is overdue and export a remediation report.
What an alert looks like
One notification, only for what you picked
The title says Active exploitation: and the product as CISA lists it. The body gives the CISA federal due date (the deadline CISA sets for US federal agencies, which many organizations use as a target) and which of your locations it affects. Tap it to open the alert.
CISA can list a vulnerability days after the vendor announces it, so keep vendor notices on too.
Illustration with an example product. Notifications look slightly different on each phone.
PatchAlert·now
Active exploitation: Fortinet FortiOS and FortiProxy
CISA federal due date Nov 6. Affects: HQ, Branch
Example push notification.
Inside the app
Screenshots show test data (CVE-2099 entries and test locations), not customer data.
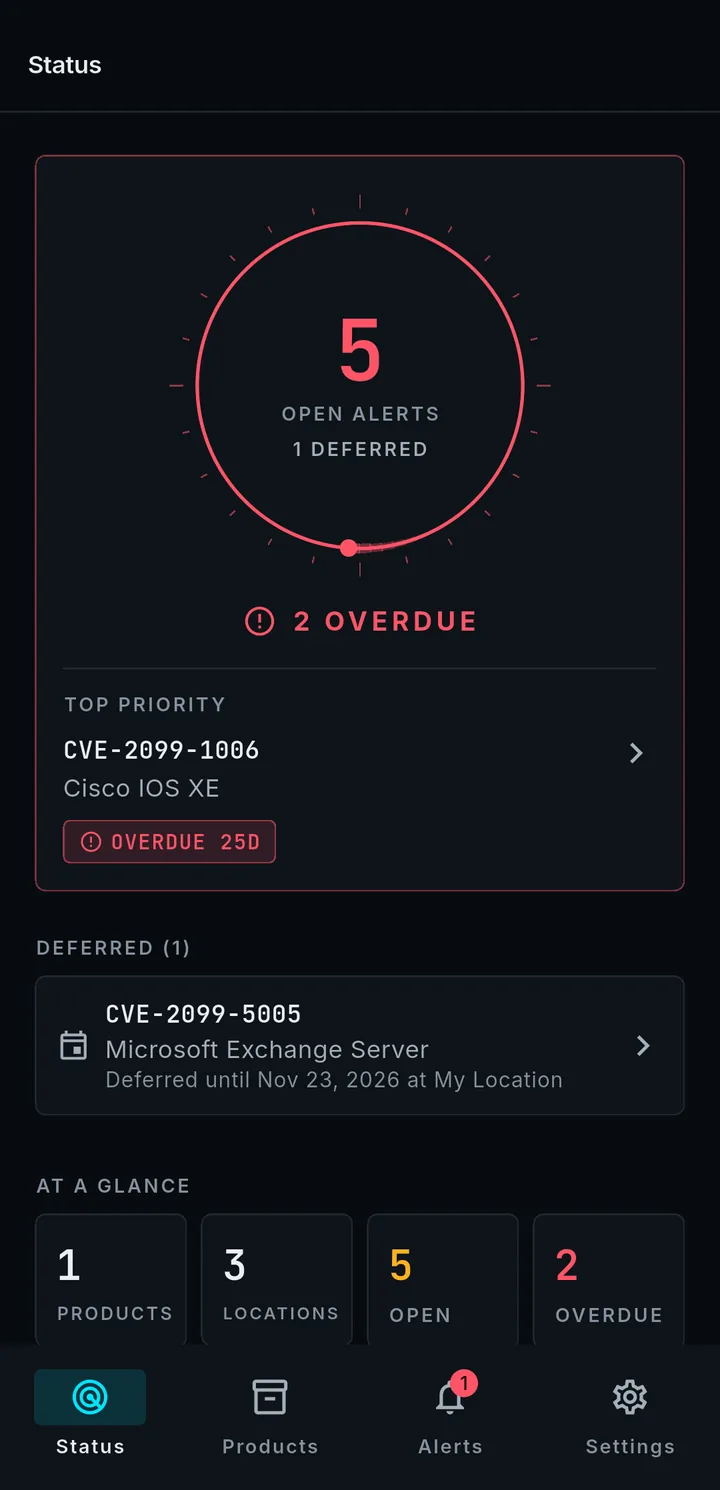
01 · Status
See what is open, and what to do first
The Status ring counts open alerts and what is overdue, names the top priority, keeps deferred alerts in their own group with their review dates, and lists catalog entries to review that were added before you started watching.
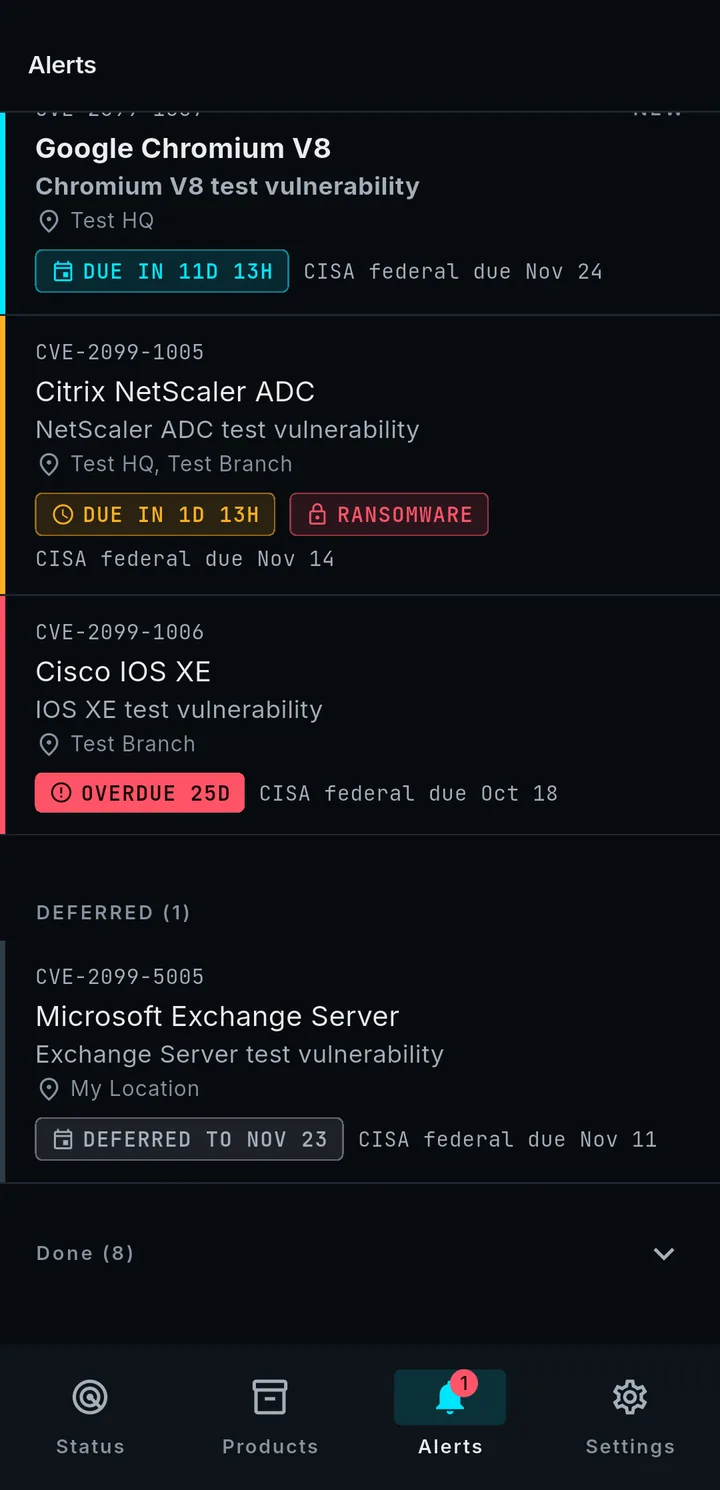
02 · Alerts
Countdowns in words, not just colors
Each alert shows a countdown to the CISA federal due date, which locations it affects, and whether it is known to be used in ransomware. Deferred alerts stay in their own group until their review date.
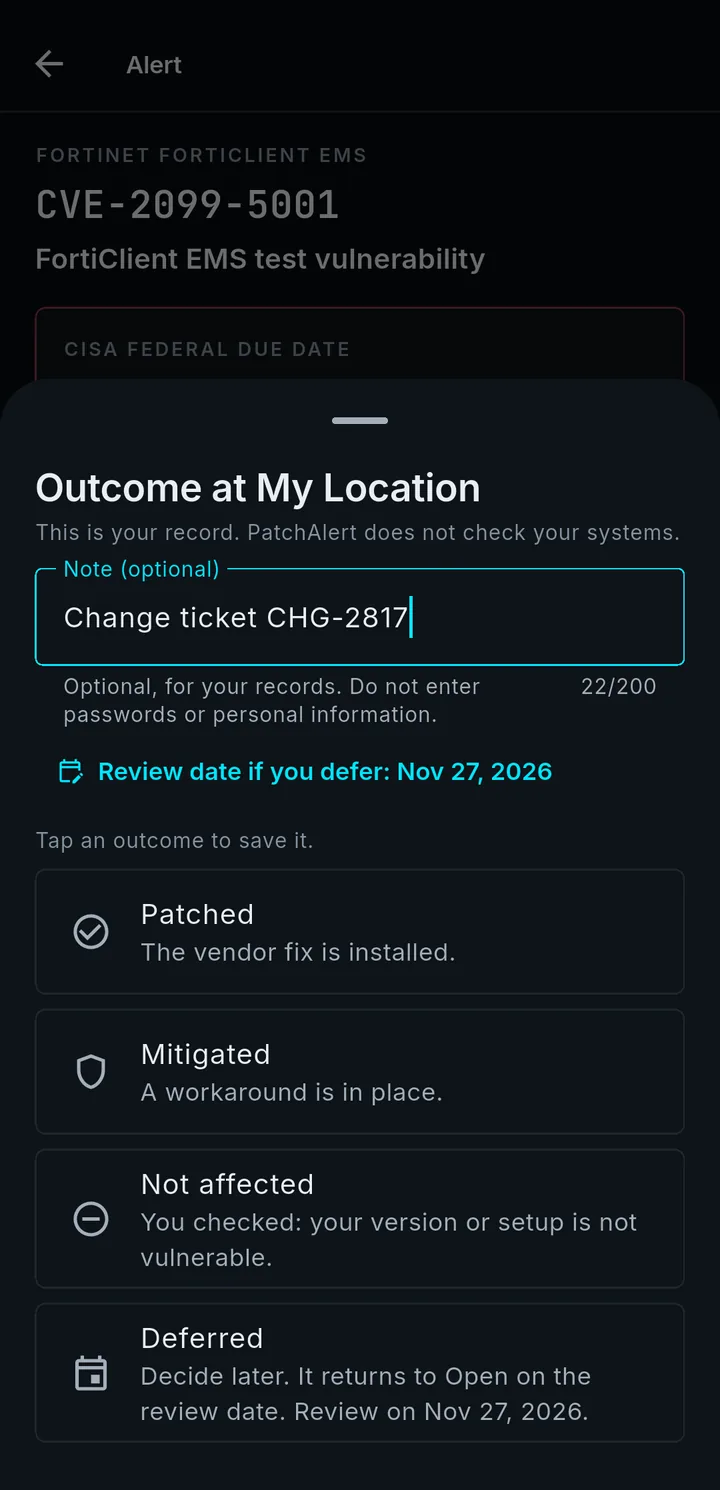
03 · Outcomes
Record what you did, in two taps
For each location, record patched, mitigated, not affected, or deferred until a review date, with an optional note. A deferred alert returns to Open on its review date. The alert shows the CISA federal due date first, and why it matched when CISA files a product under another name.
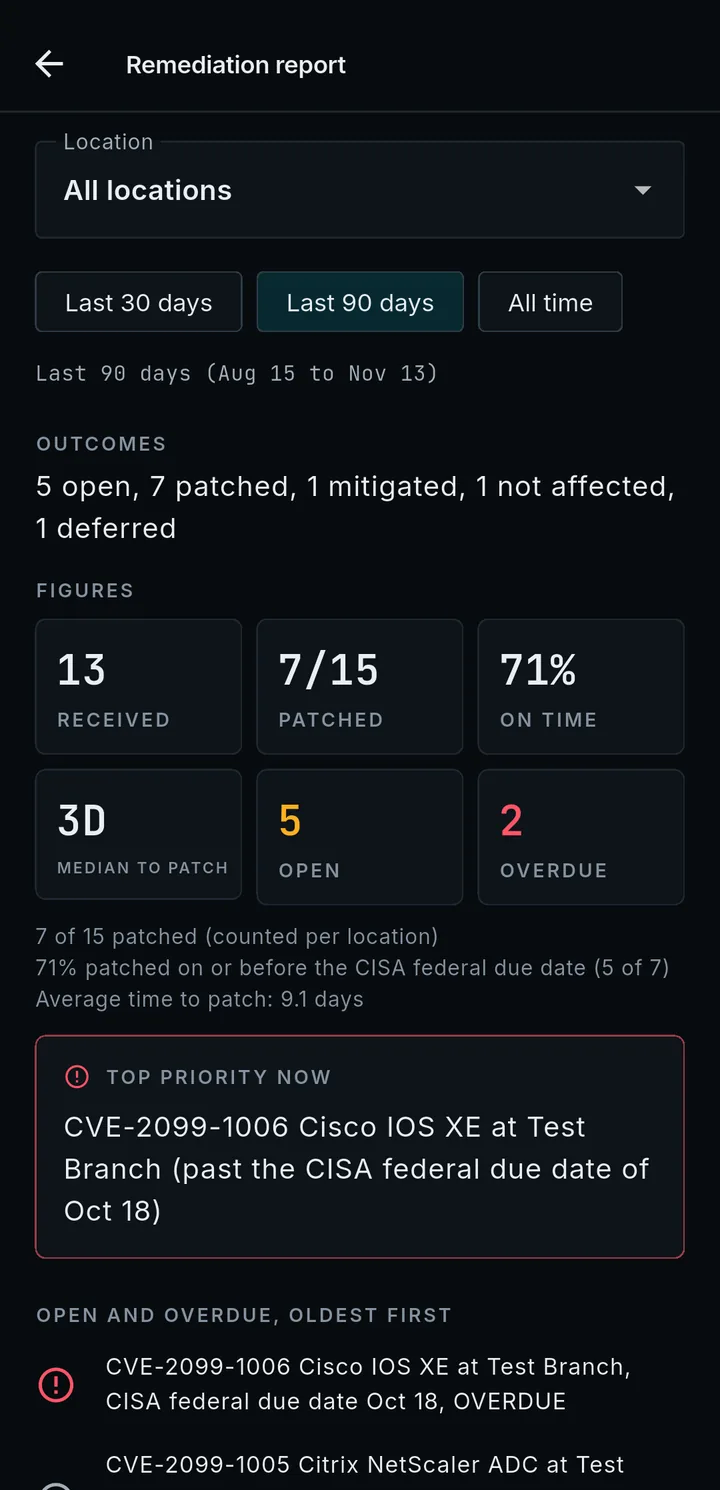
04 · Report
A remediation report for your records
Patch rate, on-time rate and median time to patch for any period and location, the top priority now, and a PDF export.
What PatchAlert does not do
PatchAlert does not scan your network or check your systems. It shows what the CISA catalog lists for the products you picked, and outcomes are what you record in the app. It is an informational service: there is no guarantee that every vulnerability is covered or that every alert is delivered, so keep following your vendors' own advisories.
Early access is free
All features are free during early access, on Android in the United States.